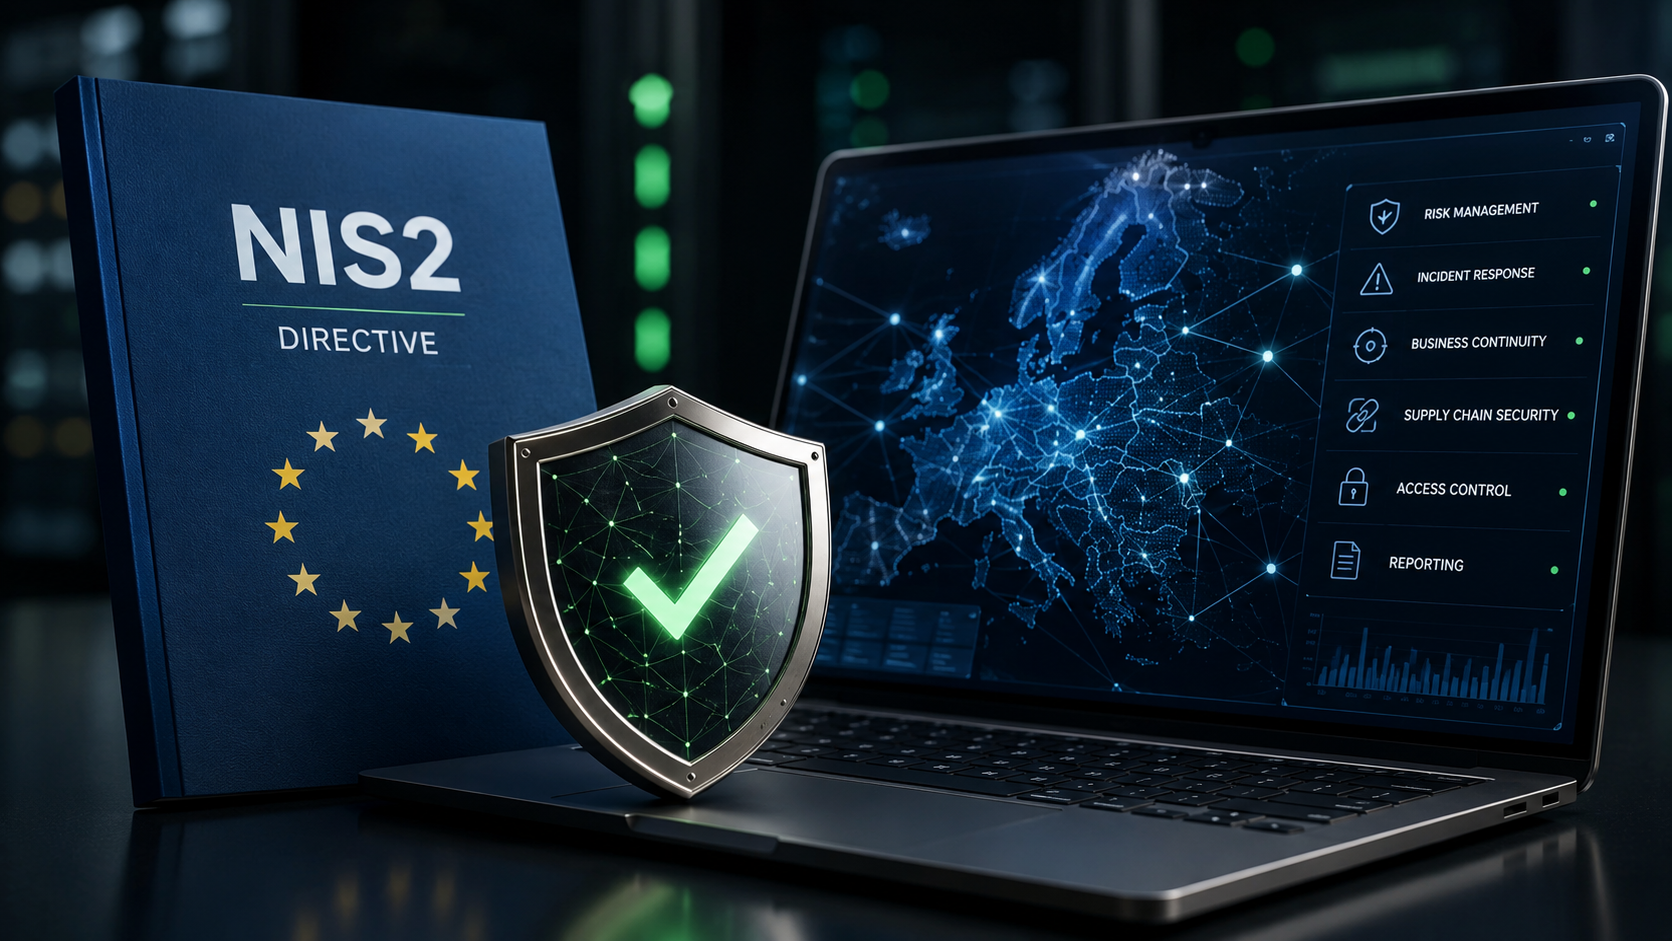
What is NIS2? NIS2 is an EU cybersecurity directive designed to strengthen organisational resilience to cyber threats and harmonise network and information system security requirements. In Poland, NIS2 is implemented through the Act of 5 July 2018 on the National Cybersecurity System, amended by the Act of 23 January 2026 (Journal of Laws 2026, item 252), as subsequently amended. The directive replaces the earlier NIS rules, extending both the range of entities covered and cybersecurity management obligations.
In practice, many more organisations must implement appropriate technical and organisational measures, manage risk and report security incidents. Responsibility for these obligations also rests with management.
NIS2 is not merely another set of formal requirements. Above all, it promotes risk assessment, continual process improvement and organisational resilience to modern cyber threats.
Why was NIS2 introduced?
The first NIS Directive was adopted in 2016 to improve cybersecurity across EU Member States. Within a few years, however, the threat landscape changed substantially. More frequent ransomware attacks, growing incident numbers and advancing digitisation showed that the existing rules were no longer sufficient.
The European Commission therefore developed NIS2, which:
- extends the number of regulated sectors,
- increases management accountability,
- introduces more detailed risk management requirements,
- harmonises incident reporting rules,
- strengthens cybersecurity cooperation between Member States.
The aim is not only better system protection, but also more effective incident response and reduced impact on business continuity.
Who does NIS2 apply to?
One of the largest changes introduced by NIS2 is the expansion of entities subject to obligations.
The directive covers organisations in sectors including:
- healthcare,
- energy,
- transport,
- water management,
- public administration,
- digital infrastructure,
- ICT services,
- postal and courier services,
- manufacturing of selected products,
- waste management.
Importantly, NIS2 obligations may also apply to many medium-sized organisations not previously covered by NIS.
The scope of obligations depends on the activities undertaken, organisational size and importance to the functioning of the state and economy. Operating in a listed sector alone does not establish coverage or entity category. In Poland, assess Articles 5 and 5a, size, legal form and exceptions.
What obligations does NIS2 introduce?
NIS2 focuses primarily on organisational resilience and reducing cybersecurity risk.
The main obligations include:
- implementing a risk management process,
- applying appropriate security measures,
- vulnerability management,
- incident management,
- ensuring business continuity,
- monitoring suppliers and supply chains,
- staff training,
- reporting incidents to the competent authorities.
Organisations should also regularly assess the effectiveness of controls and update them in response to new threats.
Risk management as the foundation of NIS2
A risk-based approach is one of the directive’s most important elements.
It is not just about implementing technical controls. Above all, an organisation should understand threats to its operations, assess their impact and plan risk reduction measures.
This process includes:
- identifying threats,
- analysing risk,
- evaluating risk levels,
- planning mitigation,
- monitoring control effectiveness.
This helps the organisation prepare for incidents and limit their operational impact.
Further reading: What Is Risk Management? A Complete Guide for Organisations.
NIS2 and compliance
Meeting NIS2 requirements involves more than implementing appropriate technical controls. The organisation must also demonstrate that it manages compliance with applicable rules and can document its activities.
The compliance process therefore plays a central role. It covers monitoring requirements, assigning accountability, maintaining documentation and preparing for audits and inspections.
Learn more: What Is Compliance and How Do You Manage It?
NIS2 and GRC
As obligations grow, more organisations are implementing GRC (Governance, Risk & Compliance) solutions.
A GRC platform connects risk, compliance, incidents and remediation in one place. This makes monitoring NIS2 compliance, preparing reports and managing the fulfilment of obligations easier.
Further reading: What Is GRC? A Complete Guide to Governance, Risk & Compliance.
Common NIS2 implementation mistakes
Implementing NIS2 should not be limited to preparing documentation or buying new tools. In practice, many organisations make similar mistakes that hinder compliance.
Common problems include:
- treating NIS2 implementation as a one-off project,
- no regular risk assessment,
- insufficient management engagement,
- no vulnerability or incident monitoring,
- documentation scattered across multiple systems,
- no accountability for requirements,
- insufficient management reporting.
As a result, the organisation meets only some formal requirements without genuinely improving security or cyber resilience.
How do you prepare an organisation for NIS2?
Preparation for NIS2 should start with an analysis of current security process maturity. Next, identify requirements, assess risk levels and determine areas for improvement.
The process typically involves:
- Identifying applicable requirements.
- Assessing risk for processes and assets.
- Evaluating current compliance.
- Developing a remediation plan.
- Assigning responsibilities.
- Implementing appropriate security measures.
- Monitoring compliance and reporting.
It is also important to review the effectiveness of implemented measures regularly and update them as threats and regulatory requirements change.
Why implement NIS2 with a GRC platform?
The number of NIS2 obligations makes compliance management in Excel increasingly inefficient. Many organisations therefore choose GRC (Governance, Risk & Compliance) platforms.
A GRC platform brings together information on:
- risk management,
- compliance,
- vulnerabilities,
- security incidents,
- audits,
- remediation,
- reporting.
Management gains a current view of NIS2 compliance, while the organisation can respond faster to threats and prepare more effectively for audits.
A practical example
Hypothetical example, not a customer implementation. A medium-sized water utility began preparing for NIS2. Initially, risk, incident, vulnerability and remediation information was kept in different spreadsheets and documents. Reporting consequently took many hours, and management lacked a complete view of compliance. The benefits described are assumptions of the example, not measured customer outcomes.
After implementing a GRC platform, the organisation structured its risk and compliance processes. All information was brought together, simplifying NIS2 compliance monitoring, action planning and reporting.
A practical first step is the NIS2 self-check, which asks whether NIS2 applies. The questionnaire is free, needs no account, and the PDF report is sent by email.
Summary
NIS2 is one of the European Union’s most important cybersecurity regulations. Its purpose is to improve resilience through effective risk management, appropriate security measures and a culture of compliance.
At the same time, NIS2 implementation should not be viewed solely as a legal obligation. It is an opportunity to structure processes, improve information security and prepare for future challenges.
Connecting NIS2 requirements with Governance, Risk & Compliance enables more effective compliance management, reduced risk and decisions based on reliable data.