Sectors covered by the Polish act implementing NIS2 (KSC)

Sectors

The Polish act implementing NIS2 (KSC) (Dz.U. 2026 poz. 252) covers essential and important entities from the sectors listed in two annexes to the Act, including public entities. The obligations are the same for all: a security management system with documentation by 3 April 2027. An essential entity carries out the first security audit of its information system by 3 April 2028 (Article 33(2) of the amending Act to the KSC Act), and subsequent audits at least once every 3 years (art. 15 para. 1). You report a significant incident to the competent CSIRT in three steps: an early warning within 24 hours, an incident notification within 72 hours of detection, and a final report within one month. An important entity that is a public entity submits only the notification within 72 hours, without an early warning and without reports (art. 12c of the Polish act implementing NIS2 (KSC)). Assets, suppliers and risks differ, which is why we describe below how CyberSonar24 helps in each sector.

01 · What every sector has in common

The same obligations, the same system

Regardless of the sector, an essential entity and an important entity run a security management system: an asset register, a risk assessment and treatment plan, incident handling, supplier-risk management, business continuity plans, training and documentation. In CyberSonar24 each of these obligations has its module, and the modules share the same registers.

  • A register of services, processes and assets with a dependency graph
  • A risk assessment with an owner, a deadline and a review date
  • Incidents and personal data breaches in one module, with notification templates
  • A supplier register with a risk assessment and contract reminders
  • Business continuity plans with a test schedule
  • Training with a certificate and a management review for the leadership

02 · Examples described in detail

Two sectors described step by step

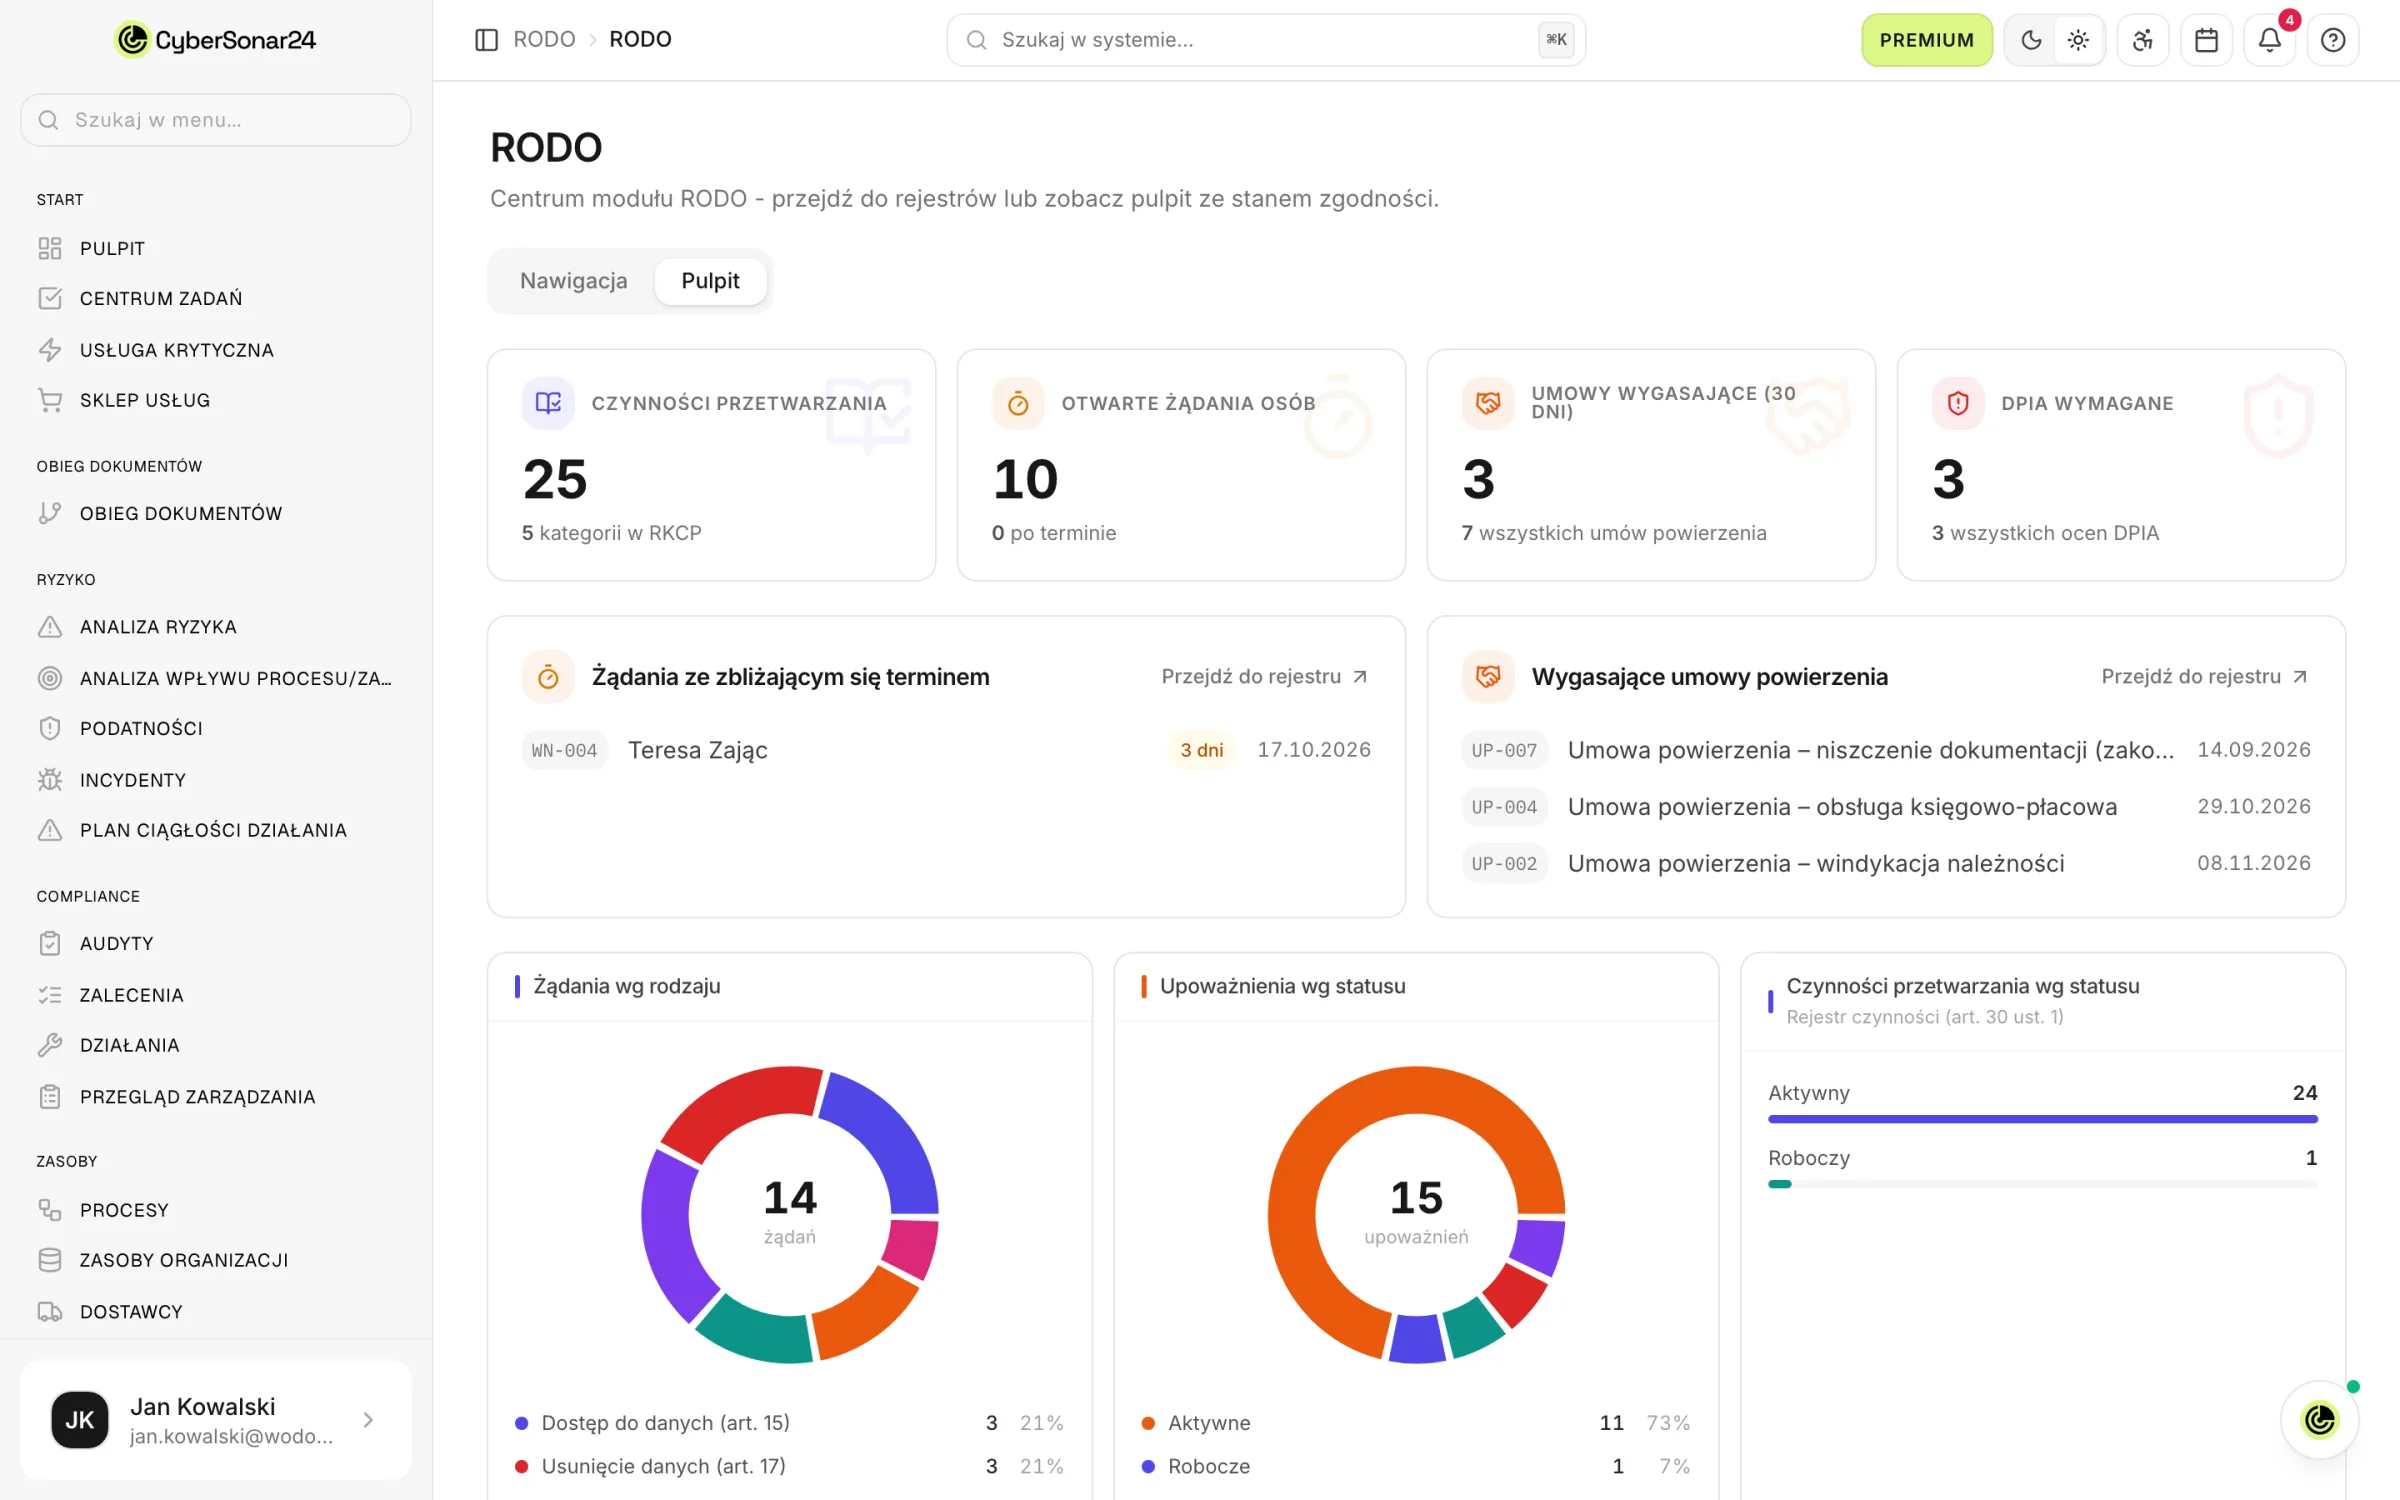
CyberSonar24 GDPR module dashboard: record of processing activities, data-subject requests and impact assessment (demonstration data)

Interface shown in Polish

Example: healthcare

Hospitals and healthcare

Hospital systems and clinical processes in one register, IT service suppliers with a risk assessment, incidents and personal data breaches in one module, training for shift staff.

  • Register of assets and clinical processes
  • GDPR: records of processing, authorisations, impact assessment
  • Business continuity plans with tests
See the solution for hospitals
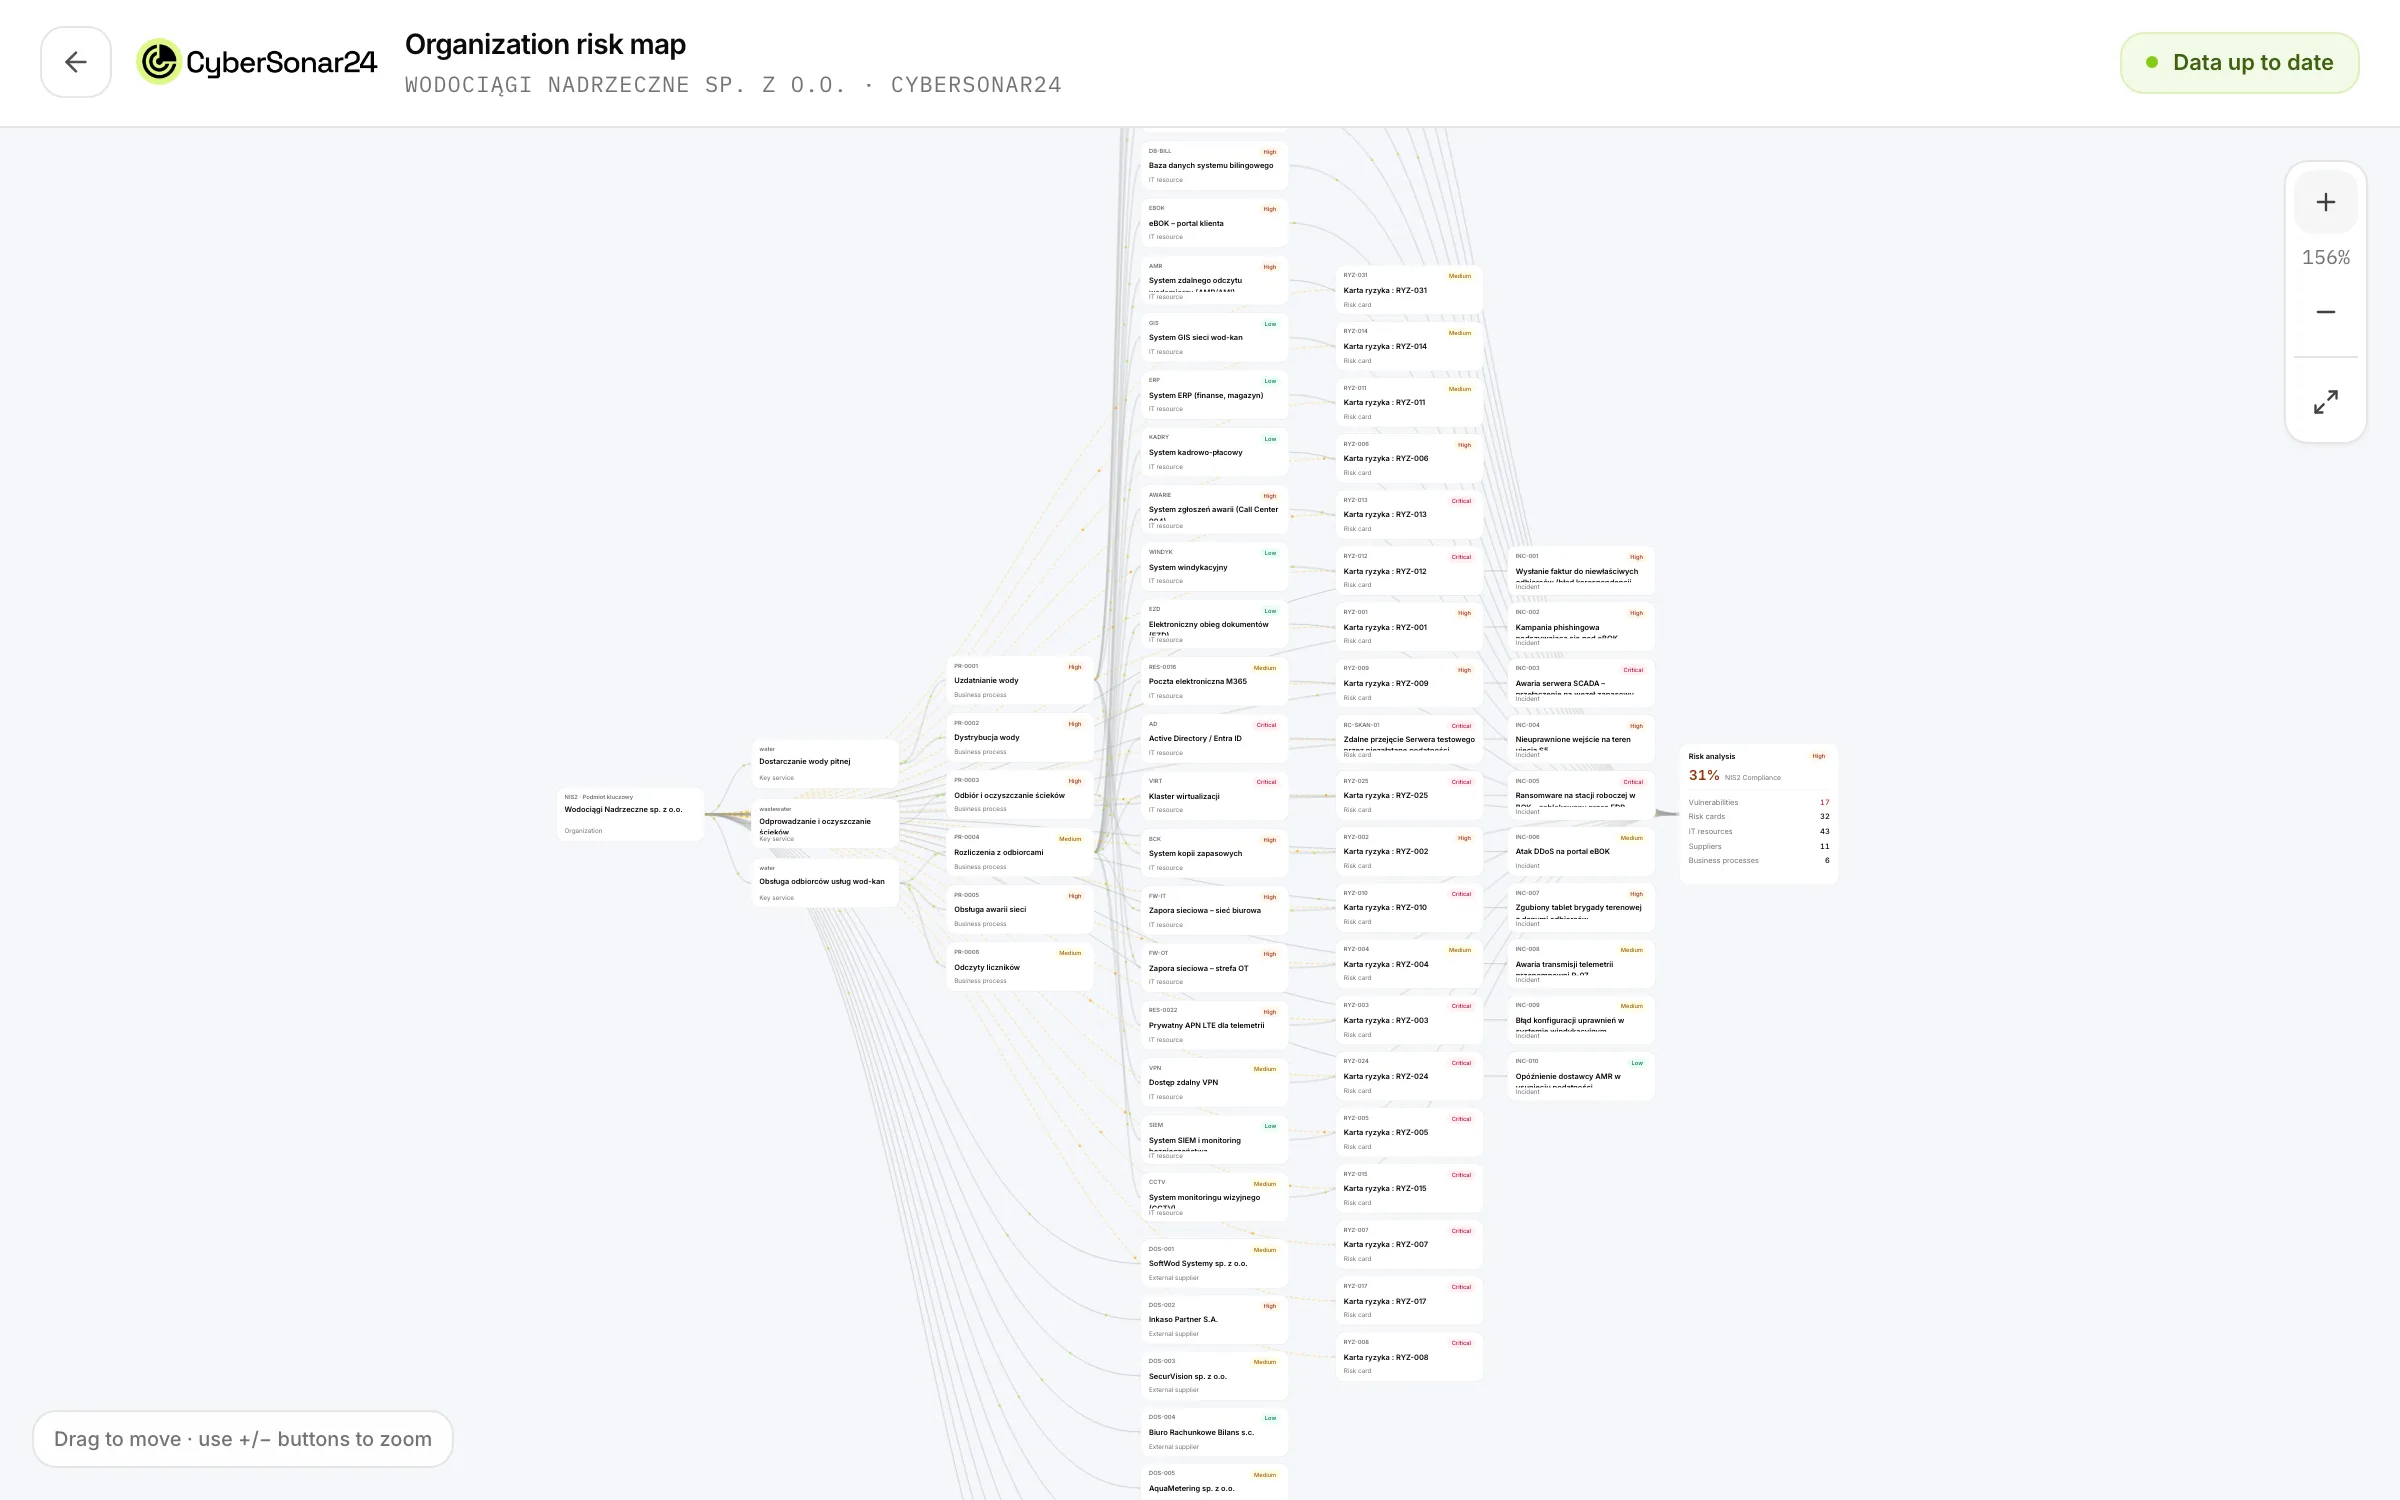
Organisation risk map in CyberSonar24: essential services, processes, IT assets and risk cards (demonstration data)

Interface shown in Polish

Example: water and wastewater

Water supply and water infrastructure

From the water intake to customer service: essential services, processes, IT systems and control systems (SCADA) linked to risks and a water-supply continuity plan.

  • Essential services and dependent processes
  • Asset dependency graph
  • Register of service suppliers with a risk assessment
See the solution for water utilities

03 · Annex 1 to the Act

Essential sectors

Sectors from Annex 1. The category is decided above all by the type of activity and the size of the entity; the Act provides for exceptions.

04 · Annex 2 to the Act

Important sectors

Sectors from Annex 2. The obligation of a security management system with documentation and the incident-reporting deadlines are the same as for essential entities. Exception: an important entity that is a public entity submits only the notification within 72 hours (art. 12c).

05 · Public administration

Public administration and local government

The Act covers public administration in both annexes. Public entities are entered in the Register of essential and important entities ex officio, and after receiving a summons they complete the data.

In local government the obligations often concern at the same time the office, its budgetary units, cultural institutions and municipal companies, for example a water, heating or waste company. CyberSonar24 lets you run them in one instance, depending on the plan (local or central): each unit has its own registers.

Local government and local-government units: the solution in detail

  • A register of assets and services of the office and its units
  • A risk assessment and a treatment plan for each unit
  • Incidents and personal data breaches in one module
  • Training of office and unit staff with a named certificate

Are you unsure whether the organisation is subject to the Act and in which category? Free Audit Zero does not require an account, and a PDF report is sent to the email address.