Why is the CISO’s role changing?
Only a few years ago, CISOs focused mainly on technical security. Their role has expanded significantly as organisational environments become more complex.
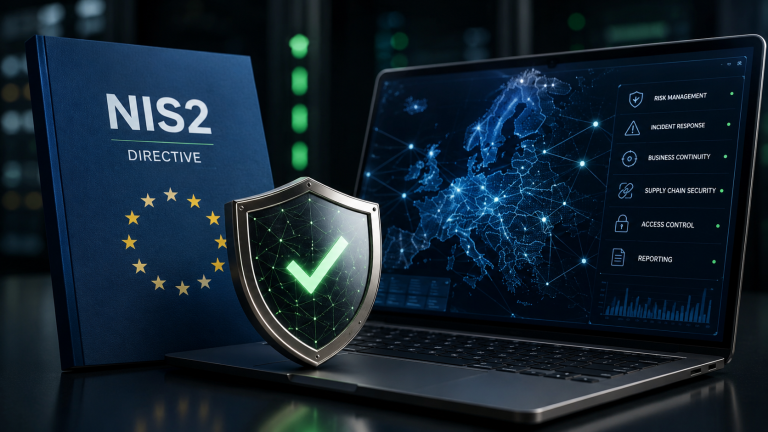
Systems, cloud services and suppliers are multiplying, while regulations such as Poland’s national law implementing NIS2 (KSC) introduce new requirements. Security is therefore becoming an organisation-wide management issue rather than solely an IT responsibility.
What does a CISO do in practice?
A modern CISO is responsible for much more than technical controls. The main task is to ensure a coherent security approach throughout the organisation.
This primarily covers risk management, incident oversight and regulatory compliance. The CISO must also work with the board and translate technical matters into business terms.
This enables informed security decisions.
Risk management as a key responsibility
Risk management is one of the CISO’s most important areas of work.
It involves not just identifying threats, but linking them to processes and assets. The organisation can then determine which risks have the greatest operational impact.
In practice, this requires a risk register, assigned owners and remediation monitoring.
Incident management and response
Incident management is another key area.
The CISO ensures a consistent process from reporting through response to root cause analysis.
The role must also ensure fulfilment of reporting requirements under Poland’s national law implementing NIS2 (KSC), requiring fast, structured action.
Compliance and regulatory requirements
New regulations have also brought compliance into the CISO’s remit.
The organisation must implement appropriate controls and document its activities. The CISO therefore oversees gap analysis, requirements mapping and audit preparation.
Requirements under Poland’s national law implementing NIS2 (KSC) are particularly relevant, covering risk, incidents and suppliers.
Why does a CISO need a systematic approach?
Security activities are scattered in many organisations. Risk data resides in different documents, incidents are handled through several tools and remediation is difficult to track.
This impedes decision-making and limits control.
The CISO therefore needs a systematic approach connecting every element in one coherent model.
The role of GRC in the CISO’s work
This is where GRC (Governance, Risk & Compliance) systems help.
They enable the CISO to:
- maintain a central risk register,
- standardise incident management,
- monitor vulnerabilities,
- oversee regulatory compliance,
- report to the board.
This structures activities and improves their effectiveness.
Working with the board and the business
A modern CISO does not work in isolation.
Cooperation with the board and other departments is essential because security affects the whole organisation. Reporting and presenting information in business-friendly terms are therefore crucial.
The board can then base decisions on actual risk.
Summary
The CISO’s role has changed substantially and now extends well beyond technical matters.
👉 In practice, it includes responsibility for risk and incident management and compliance with Poland’s national law implementing NIS2 (KSC). The Polish criminal-record requirement applies before a person undertakes the tasks specified in Article 8 or 11; Article 8f(3) recognises a valid clearance at confidential level or above. The CISO role and delegation do not remove the head’s statutory responsibility under Article 8c. KSC does not require a position named CISO.
Organisations seeking effective security management need a coherent GRC-based approach. This enables the CISO to exercise genuine control and support organisational development.